ModTracer Finds Hidden Linux Kernel Rootkits and then make visible again. Another way to make an LKM visible is using the imperius trick: https://github.com/MatheuZSecurity/Imperius …
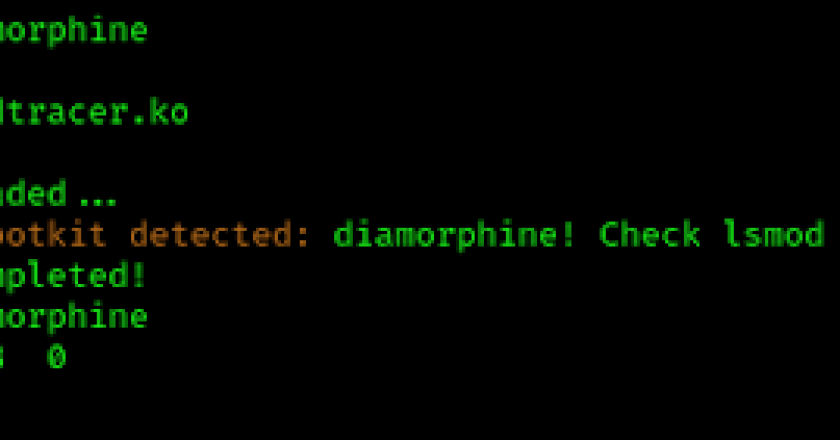

ModTracer Finds Hidden Linux Kernel Rootkits and then make visible again. Another way to make an LKM visible is using the imperius trick: https://github.com/MatheuZSecurity/Imperius …

DockerSpy searches for images on Docker Hub and extracts sensitive information such as authentication secrets, private keys, and more. What …

Reconnaissance is the first phase of penetration testing which means gathering information before any real attacks are planned So Ashok …
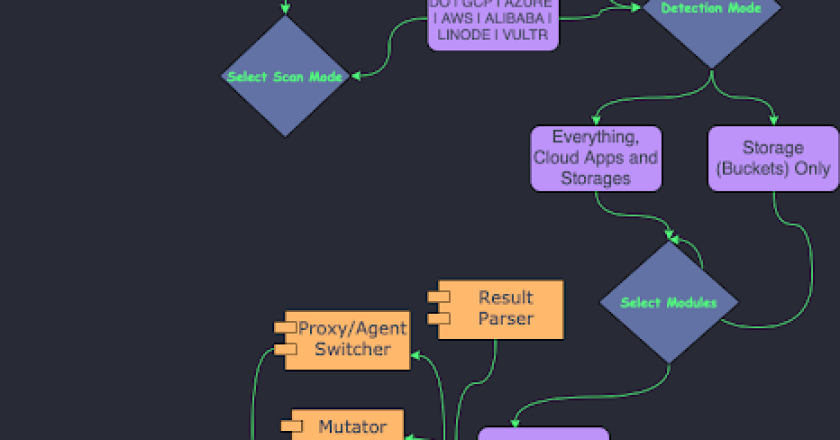
A tool to find a company (target) infrastructure, files, and apps on the top cloud providers (Amazon, Google, Microsoft, DigitalOcean, …

Tool for Fingerprinting HTTP requests of malware. Based on Tshark and written in Python3. Working prototype stage 🙂 Its main …

A vulnerable application made using node.js, express server and ejs template engine. This application is meant for educational purposes only. …
XM Goat is composed of XM Cyber terraform templates that help you learn about common Azure security issues. Each template …
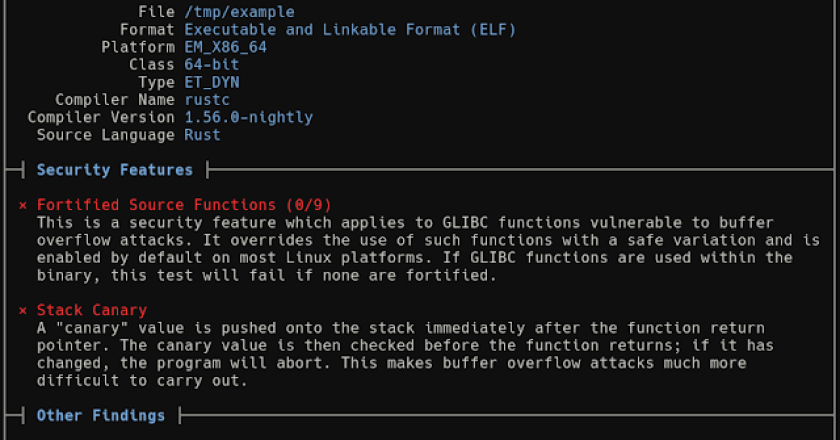
Analyse binaries for missing security features, information disclosure and more. Extrude is in the early stages of development, and currently …
A proof-of-concept User-Defined Reflective Loader (UDRL) which aims to recreate, integrate, and enhance Cobalt Strike’s evasion features! Contributors: UDRL Usage …
Shell command obfuscation to avoid SIEM/detection system During pentest, an important aspect is to be stealth. For this reason you …